Beyond the SBOM: Why the Cyber Resilience Act is a PLM Traceability Challenge
If you are a product developer, systems engineer, or PLM administrator, you have likely spent the last year hearing about the European Union’s Cyber Resilience Act (CRA) . Most of the industry chatter has focused on cybersecurity basics: secure-by-design principles, encryption, and generating a Software Bill of Materials (SBOM) in standard formats like CycloneDX or SPDX.
It is easy to see why. Security teams are comfortable with these concepts. They treat SBOM generation as a software build pipeline problem: scan the code, spit out a machine-readable file, and check the compliance box.
But an SBOM is merely a claim about what is inside your product. It is not a guarantee of what actually shipped to the customer, nor does it help you when a critical vulnerability is discovered in the wild and you have only hours to respond. That is why the CRA is not just a cybersecurity mandate—it is a massive product lifecycle management (PLM) and traceability challenge.
While many manufacturers are focusing on the December 11, 2027 deadline for full compliance (including CE marking and conformity assessments), a critical milestone has already passed. As of September 11, 2026, the CRA’s mandatory reporting obligations are officially active.
Under these active rules, if your product contains “digital elements” and is sold on the EU market, you must report actively exploited vulnerabilities and severe security incidents to the European Union Agency for Cybersecurity (ENISA) and national authorities. The timelines are unforgiving:
According to legal and industry analyses, such as those from BlackBerry, these timelines apply to products already on the market, not just future releases. This means if a vulnerability is disclosed in a component you used three years ago, the clock starts immediately.
An SBOM is a snapshot. It tells you what your engineering systems believe was designed into the product. However, physical products rarely remain identical to their digital twins over their entire lifecycle.
Consider a typical high-tech electronics manufacturer. The design starts in an ECAD tool, moves to a PLM system as an Engineering Bill of Materials (EBOM), and is handed off to manufacturing as an MBOM. Along the way, components are sourced, substituted, and updated.
When a vulnerability is announced, you do not just need to know if a specific software library or microcontroller firmware is vulnerable in theory. You need to know exactly which physical units shipped with that specific version, which customers own them, and whether a supplier substituted that component during a production run. If your product data is scattered across disconnected databases, spreadsheets, and emails, answering those questions in 72 hours is virtually impossible.
To understand why traditional approaches fall short under the CRA, let us look at how product data is typically managed versus how it needs to be managed in a post-CRA world:
| Capability | Traditional PLM & Compliance Approach | Digital Thread-Driven Compliance |
| SBOM Generation | Static text file or spreadsheet generated at the time of release. | Dynamic, live-linked SBOM tied directly to the physical product configuration and serial number. |
| Vulnerability Tracing | Manual search across ERP systems, procurement records, and engineering archives. | Instant impact analysis tracing a component from the software repository to the specific shipped serial number. |
| Supplier Substitutions | Logged in separate ERP or supplier portals; rarely synchronized back to the engineering record. | Automated change workflows that update the digital thread when a supplier swaps a component. |
| Incident Response | Panic-driven fire drill involving multiple departments, emails, and phone calls. | Structured, automated reporting workflows triggered directly from PLM and security monitoring tools. |
Product data drift is the silent killer of compliance. In electronics manufacturing, a printed circuit board assembly (PCBA) might undergo multiple component substitutions on the factory floor due to supply chain shortages or cost optimizations. A supplier might substitute an alternative microcontroller or flash memory chip.
If those changes are not fed back into the central PLM system, your official engineering record diverges from reality. Your automated security scanner might tell you that your product is safe because the official EBOM lists a secure component. Meanwhile, thousands of units are sitting in the field containing a substituted, vulnerable chip.
Software has a similar drift problem. Firmware updates, patch levels, and open-source dependencies change constantly. If your software development lifecycle (SDLC) is not tightly coupled with your physical PLM and hardware configuration management, you lose the ability to track which software version is running on which hardware variant.
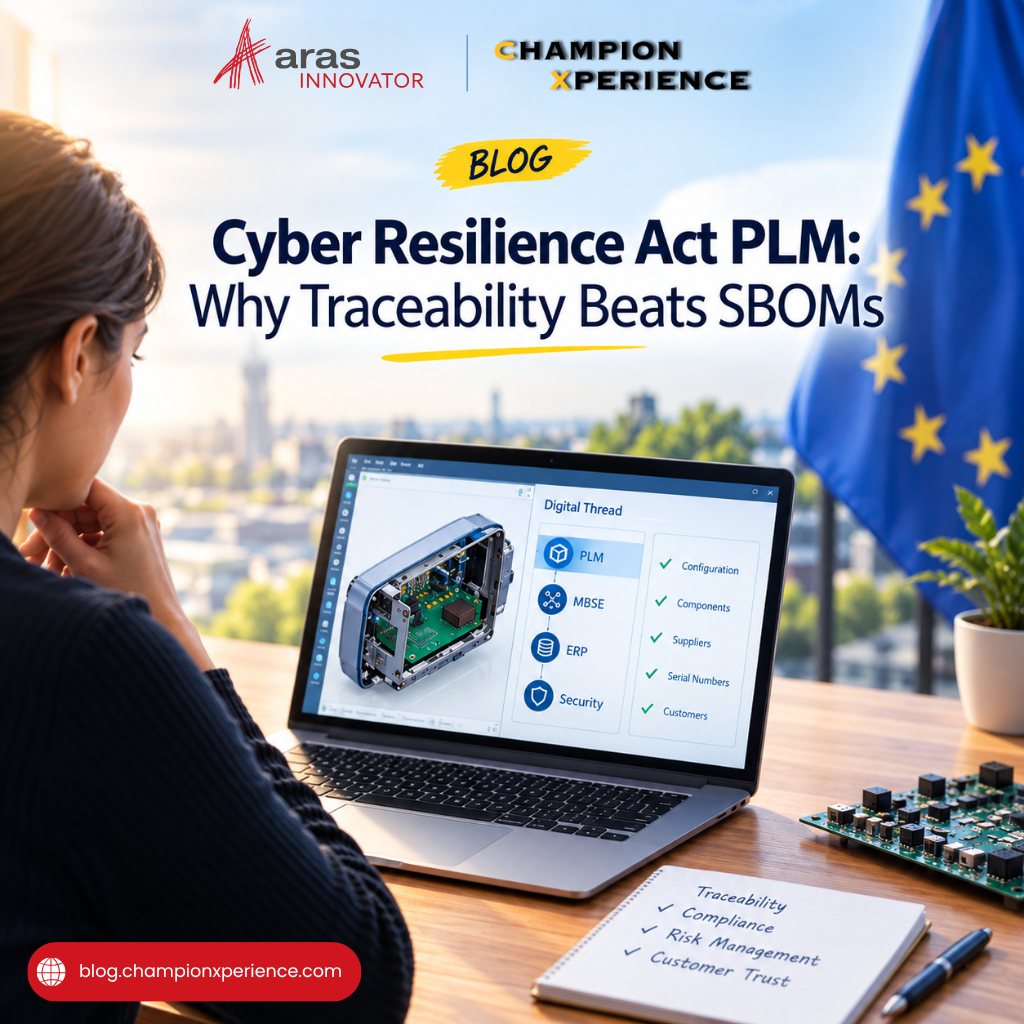
To survive the CRA’s strict reporting windows, manufacturers must build a robust digital thread that connects PLM, Model-Based Systems Engineering (MBSE), ERP, and security monitoring tools.
This does not mean you need to migrate every piece of corporate data into a single, monolithic system. Instead, it means establishing active, traceable relationships between these systems. When a software developer updates a firmware dependency, that change must automatically link back to the affected hardware configuration in the PLM system. When a supplier requests a component substitution, the approval workflow must automatically update the active SBOM.
As highlighted in recent product development insights from Dassault Systèmes, connecting multi-domain engineering data—mechanical, electrical, and software—is the only way to achieve the continuous traceability required by modern regulations. When compliance documentation is a natural byproduct of your daily engineering workflow, a 72-hour reporting deadline stops being a crisis and becomes a standard operational procedure.
Do not wait for an actual security incident to find out if your product data is ready. You can run a simulated test today to identify the gaps in your traceability chain:
This exercise will quickly show you where data silos are breaking your traceability chain. Reconciling these discrepancies now is far cheaper than facing regulatory penalties or market bans later.
The Cyber Resilience Act is changing the rules of the game for hardware and software manufacturers alike. Security is no longer a post-launch patch-up job; it is a fundamental dimension of product quality and compliance that must be managed from the very first sketch to the end of the product’s life.
By treating compliance data as an active part of the unified product record, you do more than just avoid regulatory fines. You build a more resilient supply chain, reduce engineering rework, and deliver safer, more reliable products to your customers.
Is your engineering data structured to survive a 72-hour incident response clock, or are you still relying on disconnected spreadsheets to manage your product configurations?